15:05
Telegram Desktop vulnerability allowed attackers to steal files with one click

12:33
Anthropic will ban repeated abuse of Claude under new usage rules

12:02
Apple could unveil its first touchscreen MacBook Pro on October 27

11:46
Meta bans TikTok ads on Facebook and Instagram in seven countries

11:25
Apple reportedly cuts iPhone 18 Pro orders just weeks after launch

10:59
Telegram 13.0 arrives with a redesigned interface and major Wallet changes
15:05
Telegram Desktop vulnerability allowed attackers to steal files with one click
12:33
Anthropic will ban repeated abuse of Claude under new usage rules
12:02
Apple could unveil its first touchscreen MacBook Pro on October 27
11:46
Meta bans TikTok ads on Facebook and Instagram in seven countries
11:25
Apple reportedly cuts iPhone 18 Pro orders just weeks after launch
10:59
Telegram 13.0 arrives with a redesigned interface and major Wallet changes

Telegram Desktop vulnerability allowed attackers to steal files with one click
Security researchers at BeakSec have disclosed a vulnerability in Telegram Desktop that could allow attackers to steal files from a computer and potentially hijack a user's account with a single click on a malicious link.
The flaw, identified as CVE-2026-107181, received a CVSS severity score of 8.6 out of 10, indicating high risk. All Telegram Desktop versions before 7.2.9 were affected. BeakSec demonstrated the exploit on Windows and released proof-of-concept code showing how to carry out the attack.
The vulnerability involved Telegram's handling of tg:// links, which allow users to open content directly in the messenger. Clicking such a link starts a separate Telegram process that passes the URL to the already running application through a local socket. The communication protocol uses semicolons to separate commands, but Telegram did not properly escape these characters in incoming links. As a result, a specially crafted URL could carry additional commands that the application would execute.
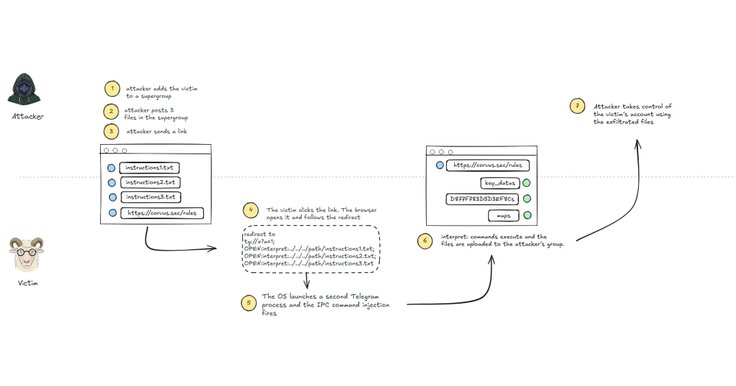
One of those commands could invoke an internal handler called interpret:, allowing an attacker to read files from the victim's computer and send them to a Telegram chat without requesting permission. Of particular concern was the tdatadirectory, where Telegram Desktop stores session data. Stealing those files could allow someone to access the victim's Telegram account without completing a new login. BeakSec said the exploit could also retrieve other files that the affected user had permission to access.
The researchers submitted their findings through the Zero Day Initiative on June 25. Telegram addressed the vulnerability in version 7.2.9, released September 17, removing the interpret: handler and introducing proper escaping for command separators. The public release notes, however, mentioned only an animation rendering fix, with no reference to the security issue.
The disclosure follows another Telegram Desktop security finding. In September, Durov's Code reported on a separate vulnerability involving the application's chat export functionality.
 Daria Ivanova
There are no confirmed reports of the flaw being exploited in real-world attacks. Users should update Telegram Desktop to version 7.2.9 or later, available through the official Telegram website, GitHub, Microsoft Store, Apple's App Store, Flathub and Snapcraft. Anyone running an unofficial client built on Telegram Desktop's code should consider switching to the official version until their provider releases a corresponding patch.
BeakSec also recommends additional precautions:
- Enable a local passcode. This encrypts Telegram Desktop's session data, making stolen
tdatafiles insufficient for immediate account access. - Limit group invitations to contacts and enable the setting that asks where to save each downloaded file.
Editor’s pick