13:30
PHP warns website owners to prepare for emergency security updates

14:26
Australia prepares legal action against social media giants over under-16 ban

13:54
You can reserve Tesla’s new Roadster in the UAE for Dh210,000

18:26
Telegram launches Money, its built-in crypto wallet: Here's how it works

15:05
Telegram Desktop vulnerability allowed attackers to steal files with one click

12:33
Anthropic will ban repeated abuse of Claude under new usage rules
13:30
PHP warns website owners to prepare for emergency security updates
14:26
Australia prepares legal action against social media giants over under-16 ban
13:54
You can reserve Tesla’s new Roadster in the UAE for Dh210,000
18:26
Telegram launches Money, its built-in crypto wallet: Here's how it works
15:05
Telegram Desktop vulnerability allowed attackers to steal files with one click
12:33
Anthropic will ban repeated abuse of Claude under new usage rules

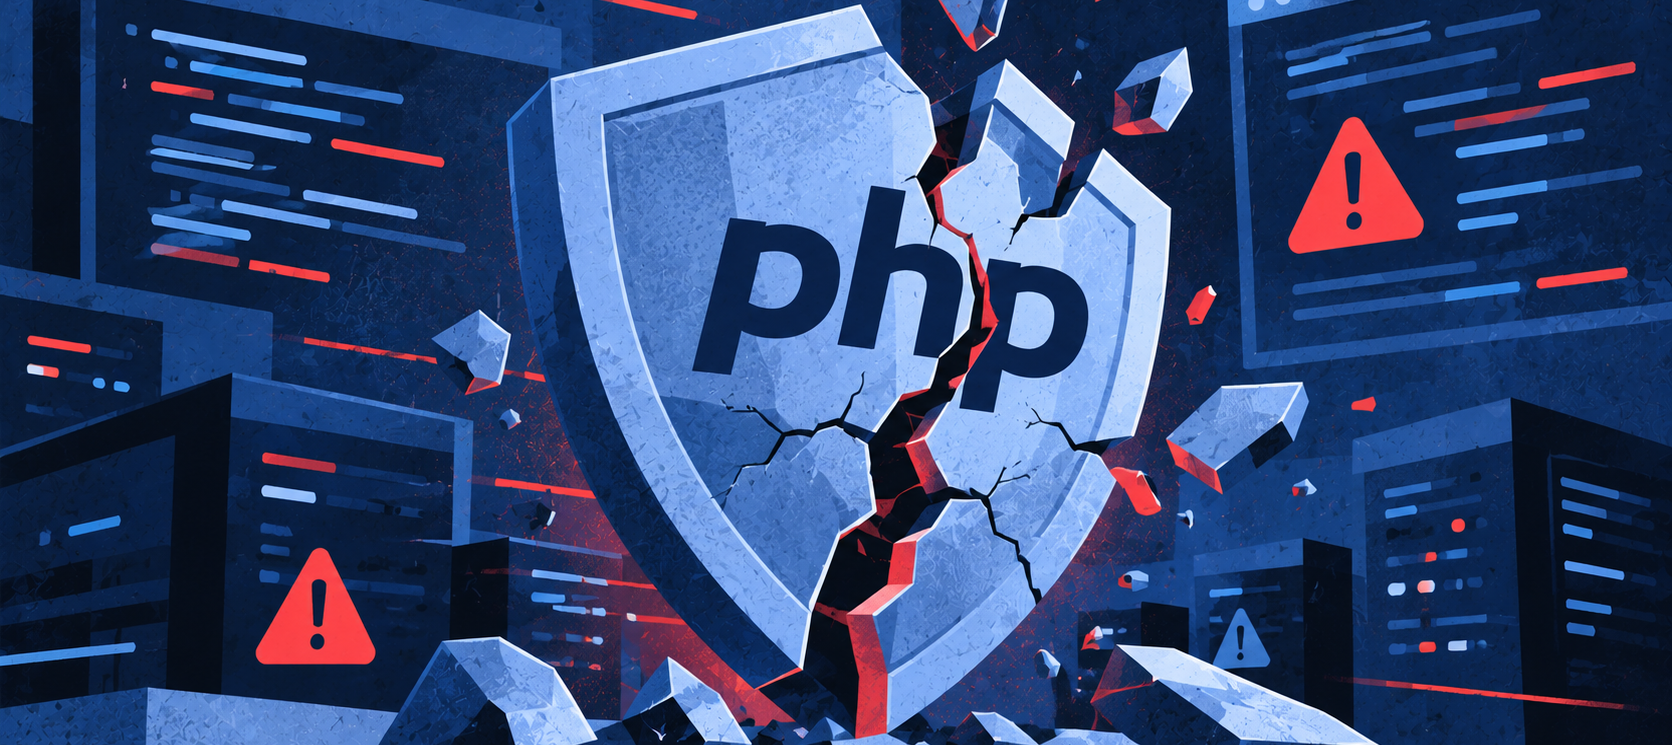
PHP’s security team is preparing emergency patches for two critical vulnerabilities and urging users to get ready to update immediately.
The release is scheduled for October 21 at 14:00 UTC, or 6 p.m. in Dubai. Both flaws carry severity scores of 9.2 out of 10 under CVSS 4.0. The team may publish the fixes earlier if technical details become public or evidence of attacks emerges.
Security company watchTowr identifies the vulnerabilities as CVE-2026-109618 and CVE-2026-109619 and describes them as remote code execution flaws. Such vulnerabilities could allow attackers to make an affected server run commands of their choosing. PHP’s advance notice does not identify the affected components or versions, with those details due alongside the patches.
The warning follows leaked claims about an attack tool called PHP2Shell. Reports suggest the flaws could affect versions dating back to PHP 5, but the development team has not confirmed that scope. The available information does not establish that every PHP website can be compromised.
PHP runs underneath widely used website software, including WordPress, Drupal, Joomla and Magento. Website owners may therefore depend on their hosting provider or server administrator to install the upcoming fixes, even if they normally manage their sites through a separate dashboard.
Huntress recommends identifying PHP installations now, arranging a maintenance window and prioritizing internet-facing systems once updates become available. Administrators should also check for older, unsupported installations that may require an upgrade to a supported branch.
As of October 21, watchTowr lists no reported exploitation in the wild. Huntress separately says it had not observed attacks exploiting these flaws in its customers’ environments as of its October 20 advisory.
Editor’s pick